Your ISP blocks port 443 to anything that is not on its allowlist, UDP looks like it has been shaped into mush, and yet DNS still resolves — because if DNS broke, the whole network would break with it. That single fact is why DNS tunnels refuse to die. In 2026 the tooling around them changed dramatically: a Go implementation with resolver health checks and eight load-balancing modes, a Rust rewrite that moved the tunnel onto QUIC multipath, and the original research implementation that everything else is measured against.
This guide compares MasterDnsVPN, DNSTT and SlipStream with commands pulled from their own repositories, not from memory. If you only need the verdict, read the next paragraph and stop.
TL;DR / Quick Verdict
If you want the fastest tunnel out of the box and you value built-in failover, use MasterDnsVPN. It ships a container image, a hardening-oriented installer, SOCKS5 on the client side and eight balancing modes; that combination simply does not exist in the other two.
If you want the smallest, most-audited codebase and you are comfortable with iptables, use DNSTT. It is the reference implementation by David Fifield, it does one thing, and it is what SlipStream explicitly credits as its inspiration.
If you have multiple rate-limited resolvers and care about header overhead, use SlipStream. It is QUIC multipath over DNS with roughly 60% lower header overhead than DNSTT, which matters enormously when every packet is paying DNS tax.
Do not use any of them for bulk transfers. A DNS tunnel is a last-resort transport for SSH, a control plane, or chat — not for pulling container images.
Side-by-Side Comparison (data pulled October 2026)
| MasterDnsVPN | DNSTT | SlipStream | |
|---|---|---|---|
| Language | Go (legacy Python variant exists) | Go | Rust |
| Stars on GitHub | 7,230 | Not on GitHub (official repo at bamsoftware.com) | 332 |
| Last commit | 2026-10-26 | Actively maintained by the author | 2026-10-24 |
| Transport model | DNS tunnel + ARQ, multi-resolver | DNS tunnel (Turbo Tunnel concept) | QUIC multipath over DNS |
| Multipath | Yes — multi-resolver with duplication | No | Yes — parallel routing across resolvers |
| Resolver health checks | Yes, with auto-disable and background reactivation | Manual | Adaptive congestion control, no health daemon |
| Client proxy | Built-in SOCKS5 / SOCKS4 | Local TCP socket (pair with ncat or tun2socks) | Local proxy + TCP forwarding |
| Official container image | Yes, ghcr.io/masterking32/masterdnsvpn | No (build from source) | Yes, GHCR |
| Setup complexity | Medium | Medium (manual port redirect) | Medium-High |
| Best for | Hostile, lossy networks | Audited, minimal deployments | Many resolvers, low overhead |
Decision Matrix: Pick in Ten Seconds
| Your situation | Recommended tool | Why |
|---|---|---|
| Censored network, high packet loss, you need it to “just work” | MasterDnsVPN | Duplication + failover + resolver health checks are built in |
| You must justify every line of code to a reviewer | DNSTT | Small, single-purpose, long track record |
| You have 5–10 rate-limited public resolvers | SlipStream | Multipath is the whole point; it was designed for this |
| You want a Docker-only deployment on a VPS | MasterDnsVPN | The compose file is 11 lines |
| You are tunnelling an SSH session, not a browser | DNSTT | Zero extra moving parts |
| You need 100 Mbit throughput | None of these | Use a real proxy; see our proxy platform comparison |
MasterDnsVPN: The Batteries-Included Option
MasterDnsVPN is the project that made people look at DNS tunnelling again in 2026. Instead of asking you to wire up port redirection by hand, it ships a server container that terminates the tunnel, a per-architecture client (AMD64, ARM64, ARMv7, ARMv6, ARMv5, RISCV64, MIPS, MIPS64 and more), and a configuration surface that exposes almost every subsystem.
The official compose file from docker/docker-compose.yml in the repository is deliberately tiny:
| |
Two things matter here. First, DOMAIN must be the delegated subdomain you created with an NS record — for example v.example.com pointing at ns.example.com, which in turn has an A record for your server. Second, everything stateful lives in /data: keys and config survive container replacement, which is what you want, because losing the encryption key means re-enrolling every client.
If you prefer the host-installed path, the project provides an installer:
| |
When it finishes, the encryption key is printed to the terminal and written to encrypt_key.txt next to the binary. Treat that file like a private key — because it is one. Then open the DNS port:
| |
On the client side you download the matching architecture bundle, point it at your tunnel domain with the key, and use the built-in SOCKS5 listener to route traffic. The practical advantage over the alternatives is that failure handling is not your job: the client can balance across resolvers in eight different modes, duplicate packets to trade bandwidth for reliability, and automatically disable resolvers that stop answering — then quietly bring them back when they recover.
Verdict: pick this when the network is actively hostile and you cannot babysit it. The trade-off is a much larger configuration surface than DNSTT, and behaviour that is harder to reason about when something goes wrong.
DNSTT: The Reference Implementation
DNSTT does not try to be a product. It is two binaries, dnstt-server and dnstt-client, plus documentation that assumes you know what an NS delegation is. That minimalism is exactly why people still deploy it in 2026.
Generate a key pair first — this is the step everyone forgets:
| |
The server then forwards tunnelled TCP to a local service. In the reference example that service is a bare netcat listener on port 8000:
| |
Because binding port 53 directly is often impossible (something else on the box usually owns it), the documented pattern is to run on 5300 and redirect:
| |
The client supports plain UDP, DNS-over-HTTPS and DNS-over-TLS, which is the detail that makes DNSTT usable on networks that only allow encrypted resolvers:
| |
Verdict: DNSTT is the right choice when the tunnel is a small, auditable component inside a bigger system. You will write your own supervision, health checks and rotation. If you want those features without writing them, look at the other two.
If you are new to tunnelling over DNS at all, the lower-level mechanics are covered in our iodine vs dnscat2 comparison, which is still the best explanation of why DNS tunnelling works in the first place.
SlipStream: QUIC Multipath, Wrapped in DNS
SlipStream is the newest of the three and the most interesting from an engineering standpoint. Its premise: a single public resolver will rate-limit you into the ground, so stop pretending you can squeeze a session through one. Instead, encode a QUIC multipath session inside DNS queries and spread it across as many resolvers as you can enumerate.
The project states two headline claims, both from its own documentation: 60% lower header overhead than DNSTT, and adaptive congestion control that responds to rate-limited resolvers rather than assuming a fixed bandwidth. Architecture diagrams and benchmark charts live in docs/assets/ in the repository, and the docs site is at endpositive.github.io/slipstream.
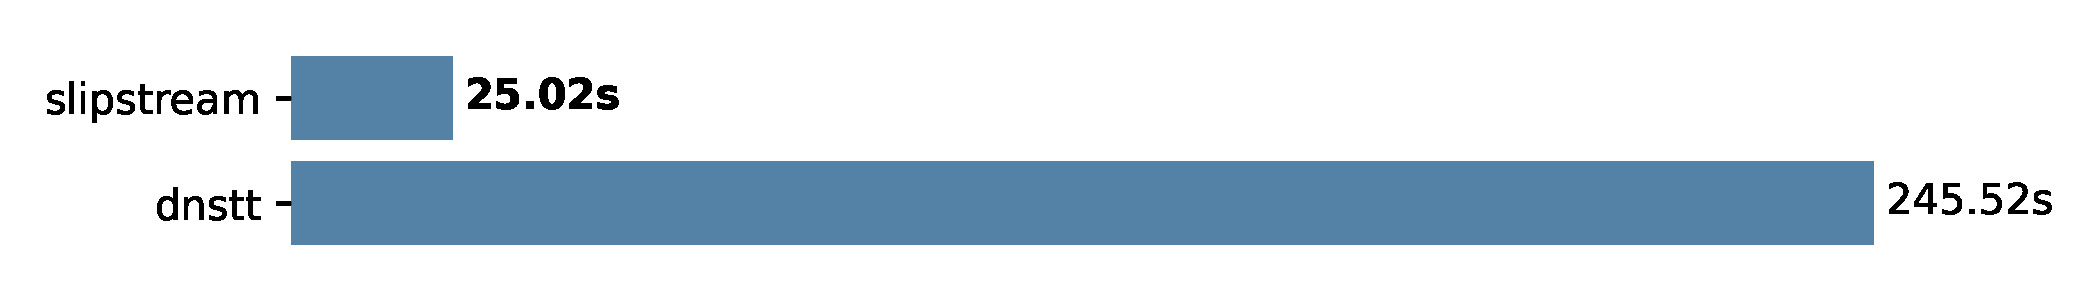
Deployment is binary- or container-based:
| |
Because the project is young, the operational documentation is thinner than MasterDnsVPN’s: expect to read source when you need to debug an unusual resolver. The payoff is real though — if your tunnel dies every twenty minutes because the resolver you picked throttles you, multipath is the feature that fixes it, and neither DNSTT nor the older tools offer it.
Verdict: the strongest throughput story of the three, the weakest operational maturity. Perfect for experimentation and for networks where resolver throttling is the dominant failure mode.
Pitfalls That Will Cost You an Evening
Port 53 is almost always taken. On modern Linux, systemd-resolved holds 127.0.0.53:53. Either bind your tunnel to a dedicated IP, use the redirect pattern, or disable the stub listener. Same for Pi-hole or AdGuard Home on the same host — they will fight you, and the symptom is a silent “tunnel connects but nothing flows”.
NS delegation is not the same as an A record. You need a subdomain whose NS record points to your server’s name, and that name needs an A record. Verify with dig v.example.com NS and then dig @ns.example.com v.example.com A before blaming the software. Propagation can take minutes to hours, and a surprising number of “broken” tunnels are just caching.
MTU and fragmentation will bite you first. DNS responses have practical size limits; when the path MTU drops, tunnels that do not handle fragmentation well simply stall on large transfers. MasterDnsVPN explicitly advertises tolerance for very small MTU, which is one of the few claims in this space that you can feel immediately in real use.
Resolvers rate-limit, and they remember you. A tunnel that works at 9am can be dead at 3pm because your favourite resolver started dropping queries from your prefix. Health-checking and multi-resolver routing are not luxuries; they are the difference between a demo and a deployment.
Monitoring cuts both ways. DNS tunnelling is detectable — plaintext UDP tunnels especially so, which the DNSTT documentation itself notes. If your threat model includes a network operator who actively hunts tunnels, throughput is not your main problem; traffic shape is.
Client binaries are architecture-specific. MasterDnsVPN publishes at least ten Linux builds including MIPS and RISC-V. Downloading the wrong one produces confusing exec errors on routers and single-board computers, which is exactly where people deploy these.
For the network-operator side of this coin — how traffic gets classified and shaped — see our Tor relay and pluggable transport guide.
FAQ
Is a DNS tunnel the same thing as a VPN? No. A VPN creates a network interface and routes packets through it. A DNS tunnel encodes your traffic inside DNS queries to one authoritative server you control. Some implementations expose a SOCKS5 proxy so applications can use it like a VPN, but the underlying transport is entirely different — and much slower.
Can I run MasterDnsVPN alongside Pi-hole or AdGuard Home on one server?
Yes, but not both on 0.0.0.0:53. Give the tunnel its own IP address, or run the DNS filter on one IP and the tunnel on another. Running the tunnel behind a redirect rule from port 53 also works if the filter is not already bound there.
Why does my tunnel connect but no traffic flows?
In order: the NS delegation is wrong or not propagated, the public key on the client does not match server.pub/encrypt_key.txt, the firewall allows TCP 53 but not UDP 53, or the local proxy port is not the one your application is using. Check those four before touching configuration files.
How fast can these actually go? The honest answer is “slow, and it depends entirely on your resolvers”. The MasterDnsVPN repository publishes local benchmarks around 0.27s for a 10MB download versus 2.49s for DNSTT on the same test, but those numbers say more about protocol overhead than about what you will see over a real recursive resolver across the internet. Plan for interactive use, not transfers.
Is SlipStream compatible with DNSTT servers? No. They implement different protocols. SlipStream credits DNSTT’s Turbo Tunnel concept as inspiration but shares no code, so server and client must come from the same project.
What happens if my server’s IP changes?
Every client breaks until DNS updates and caches expire. Use a stable hostname in the NS record, keep the TTL low during initial setup, and remember that some resolvers ignore low TTLs anyway.
💰 想测试你的市场判断力?我用 Polymarket 做预测市场交易——这是全球最大的预测市场平台,从大选结果到技术监管时间线,什么都可以押注。和赌博不同,这是真正的信息市场:你懂的信息越多,胜率越高。我靠预测技术相关事件的走向已经赚了不少。用我的邀请链接注册:Polymarket.com